Showing posts with label network. Show all posts

Friday, 10 October 2025

XVE Game Engine: Thinking about AOE Damage Effects

I'm back on my home game engine and I need an area damage effect, which can apply to all the members of a team/party.... The trouble?  How to synchronize this over a network connection.

First of all, I know for certain that the server running my game world knows the center of the effect, and it knows the radius of the effect.  And it does tick the effect application against each player whether their client can visually see the effect - it appears in their combat log text immediately.

So the mechanics are there, the clients however, all run at different rates, they're in different locations world wide, with different latencies to the servers source of truth.... And so I need to now think about how I am going to tackle the issue of each player seeing an effect.

Simplicity first, the effect is just going to be represented by a wireframe sphereoid, it'll be a smooth shaded sparkles dripping effect later.

This quiets my engine engineer smooth brain some what and I now just need to synchronize the expansion from the center to the maximal radius of the effect, this will turn up at the clients from the server at any time after the effect is registered as affecting the players on the server... This maybe unfair, however, there is reason behind this in the design - the player will know the effect is going to be cast as there is pre-warning from the caster... They need to learn that and move before they see the effect basically.... That is, they need to be smart.... I know I know this is a cheap answer, but I am all about cheap answers to problems today - and in my gameplay loop, seeing the caster "spit" this effect and moving before it expands into a cloud of hell... is pretty rewarding.

So I have a time point, on all clients they know when the effect begins, they know the maximal extent and they know the center of it....

What I am thinking about now is the client side only, so without any network traffic, an entity definition for the effect which the client has pre-loaded into some dictionary of effects to execute, and this contains a rate per millisecond from the start time and the effect system has to linear interpret along the line.

I am thinking about designing some form of easing curve authoring for the client effect system - and I'll likely reuse this in the animation system - whereby I can try different easing curves.
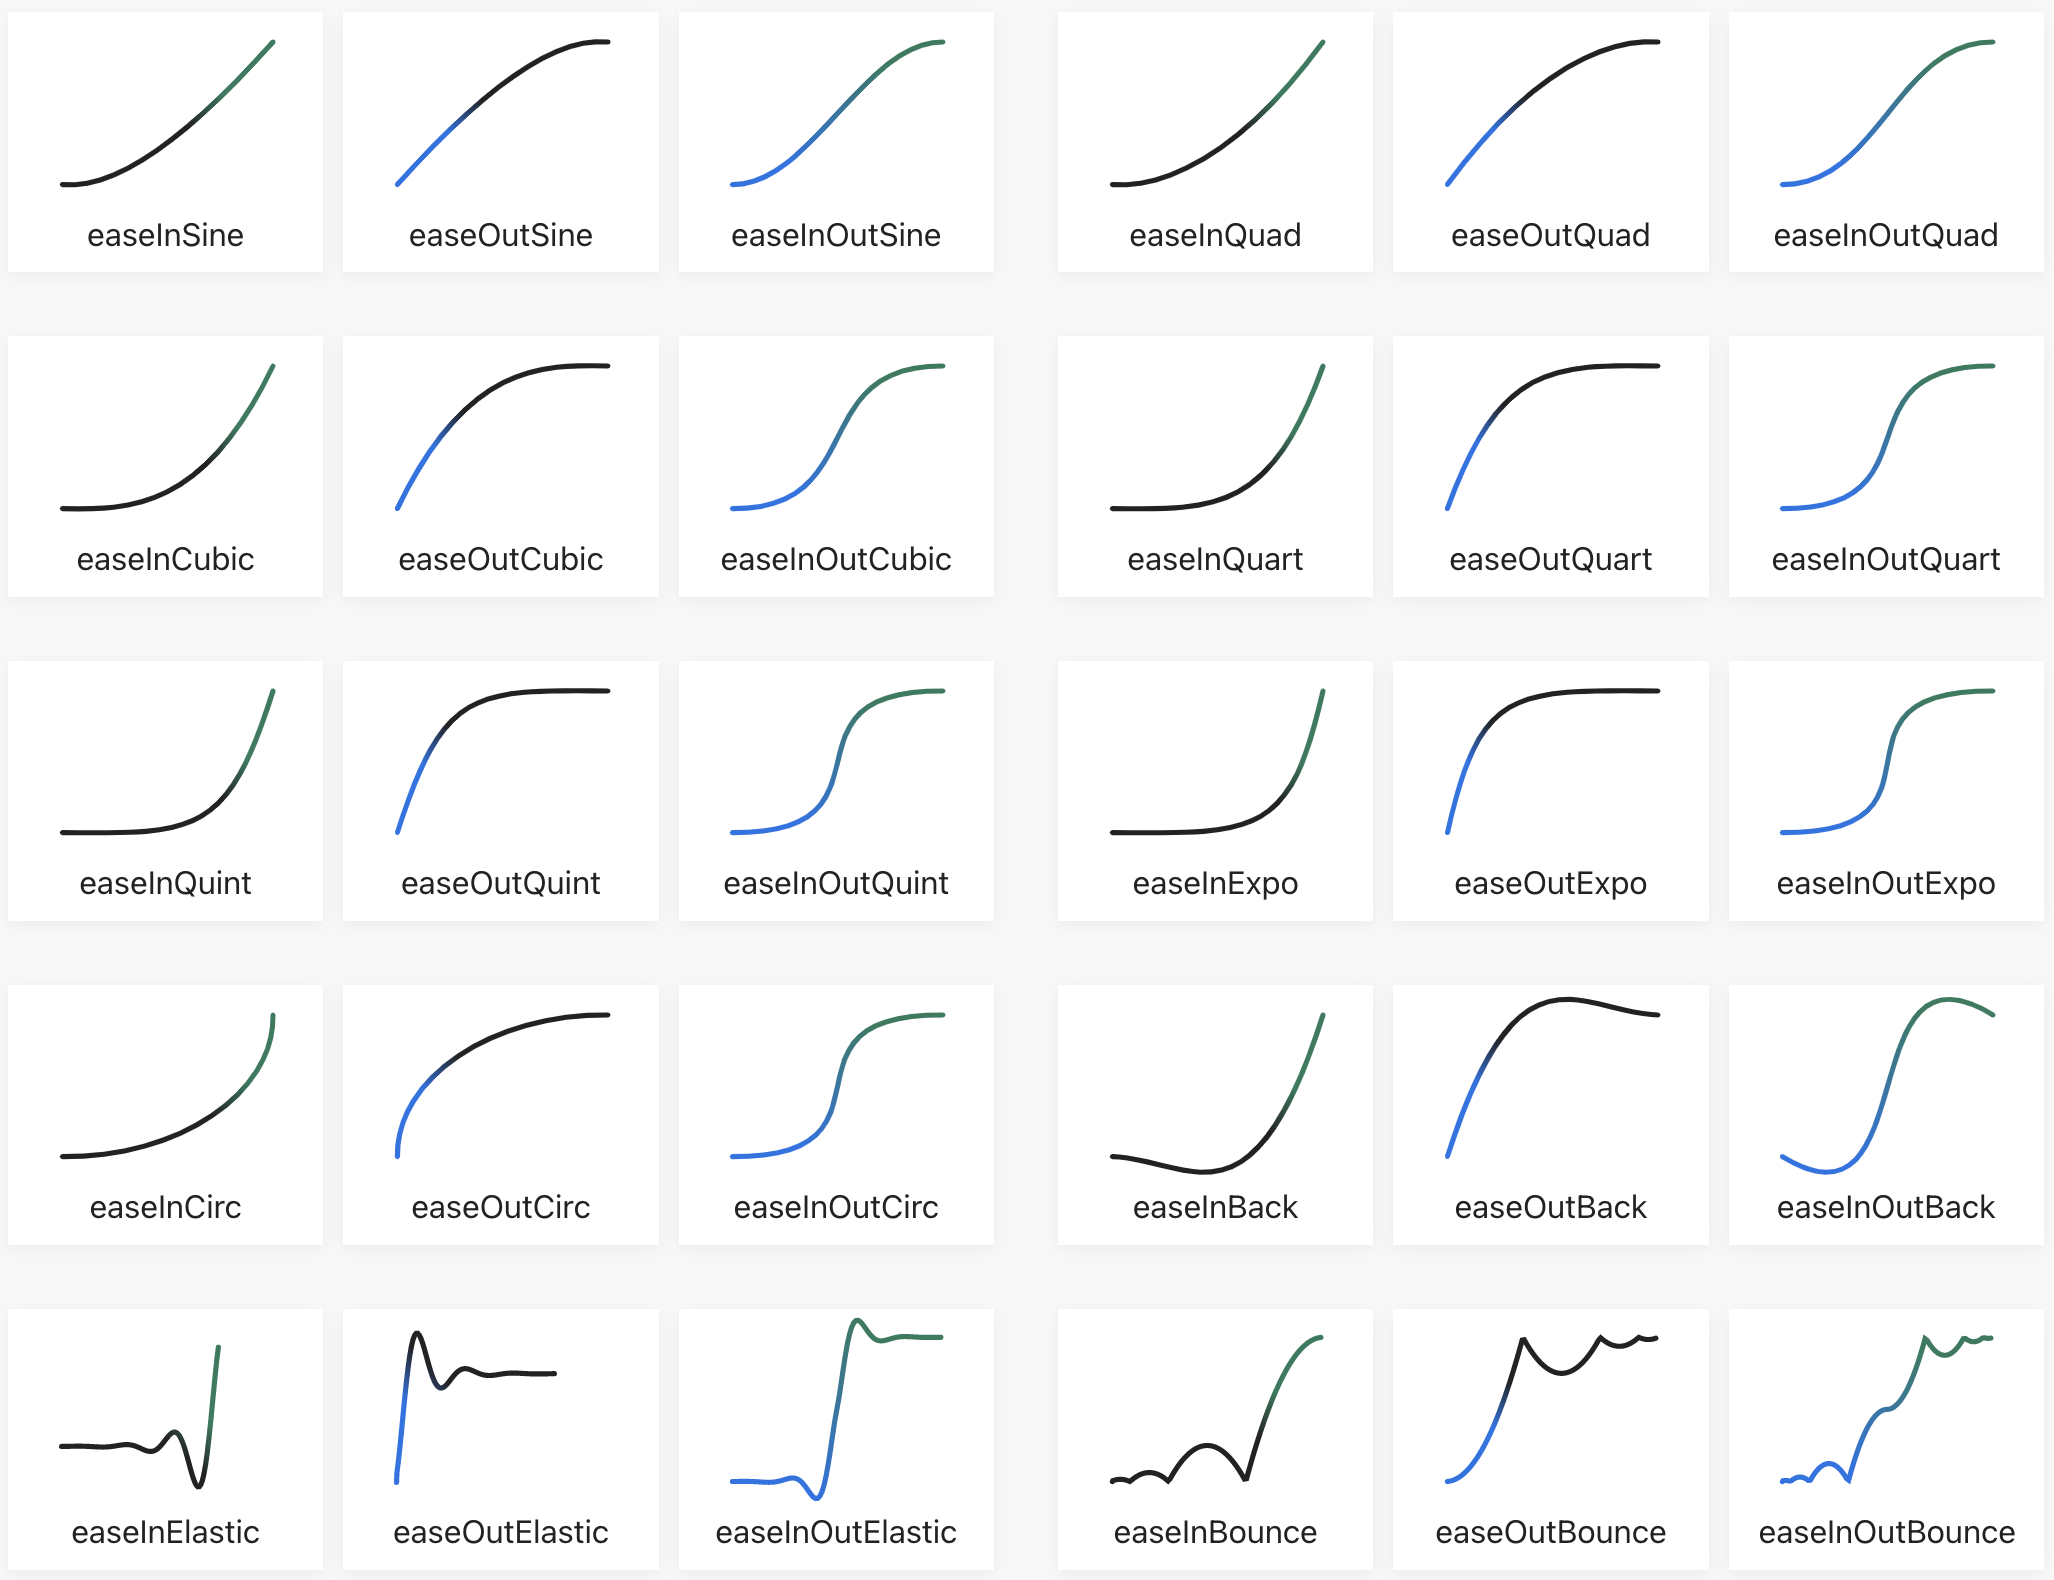

 The system interpreting along the line could be more than a lerp too, again that'll be down the line.

Replaying, reversing or otherwise on such a defined effect is going to be quite interesting as reversing the delta will allow me to contract it again.... Though time-line ordering is to be forwards chronologically only for my game play, that maybe a feature I want to play with in future.

What's the problem then?  Yeah, it sounds like I have a handle on what I want, except.... I've assumed all the way through my thinking that the effect is fixed, known and defined up front.... The problem?

I want to scale the effect with the power of the caster, and this is not known up front, sure I can just add a float and multiply by 0.5 for half power or anywhere along that scope, heck I could even scaled the enemies power by some easing function as well and combing the power function along that line with the rate of the effect.... So there are answers to be had.

My problem is randomness, when it's random, things look wrong, they don't feel right when playing them and the rewarding feeling I had from the fixed function gameplay doesn't turn up... It's in some fort of metaphysical uncanny valley which I can't quite explain doesn't feel right.

I will have to play about some I feel.... 

Sunday, 10 February 2019

The Lost Router

Its gone... Just gone.. Puft... Up and gone... I remember it in the box, I remember packing it... Puft, gone, where is it?... Have you seen it?....

LOST


LinkSys WRT AC1900

Responds with the SSID "XelNet"

Likes to sit on the side serving internet pages to the house and the occasional belly rub....


It's just lost.. I've come this weekend to sort out my network situation, so I've finally gotten an afer market ADSL modem to replace the BT Home Hub, I've got a powerline network adapter to carry network upstairs to the wired office (rather than running wires through ceilings just yet).

I've gotten the hub for the garage and the hub for the office sorted... And all the smaller ethernet cables all crimped to perfect length to stop wires trailing all over under my desk and behind the TV.

But, then I go to find my router and it's just missing... I remember boxing it back in it's own box on moving day, I remember doing that.... I remember it distinctly.

I think it went into my car, not the wifes... My car is now clearly empty, I emptied it... So I've been through EVERY box in the garage three times, been through the loft twice, I've been through every nook and cranny I can find...

My thoughts are that maybe, perhaps, it's at the in-laws house, I've asked them to look and they just said "no"... But I think it's there by their PC and they don't realize the box which looks like theirs is mine.

So frustrating!


--------

Update, the wife came with to go through EVERY box in the garage with me... Guess what... No, no... She didn't come up smug (I knew you'd think she would)... The thing is still LOST... GONE LOST VANEEEEEEEESHED.... Gah.

I think I have to go look at the in-laws.

Monday, 19 June 2017

Bash : Power of Pipes

Subtitle: "Get IP Address Easily"

When I say easily, I mean not so easily, but with the proper tools... Let me explain, it's been one of those days... I've a remote server running some flavour of Linux, and no-one knows it's remote IP Address, they all SSH into the box run "ifconfig" and note down the value, they then plug this into a config (or worse still were baking it directly into some code) and running their services....

The trouble of course being, years later, they're no-longer the programmers nor maintainers of this machine, I am...

And to be frank whenever the IP address changes I don't want to recompile their java code, nor use vi to edit the various configuration files, I want a script to at least update the settings automatically.

I therefore changed their code to load the IP address, not hard code it, and used some other scripts to put the IP address into the config file at boot...

The first line of that script is what I'm going to document here... so it starts:

#! /bin/bash
ifconfig | grep inet | tr ' ' '\n' | sed -u '/^$/d' | head -2 | tail -1 > ipaddress.txt

This script gives me a single line of text with the IP Address in it, for the one and only adapter in the machine, if you have multiple adapters you'd have to play about with the grep inet to select the row you want with a head & tail call before moving into the  final location, or whatever...

I wrote this up however, and immediately started to use the IP address.

The net result was a request to explain all this functionality to a colleague... Here's what I came up with.

ifconfig gets us the adapter information...
grep strips off lines we don't want only giving lines for the inet adapter
translate turns spaces into new lines
the sed call removes the blank lines, giving just the IP address and some guff
the first adapter IP address is therefore always the second line of this output
we select the first two lines with head
then select only the latter of these two with tail
and write this to a file

Her reply... "What are the Lines?"....

"What lines?"...

"These | things"....

"They're pipes, I'm piping the information from one program to the next..."

"Oh"

"Do you know what pipes do in Unix and Linux?"

"No"

I sent her to this video... https://youtu.be/XvDZLjaCJuw?t=5m15s

Monday, 2 January 2017

Administrator : Show Network Abuse...

As a network boffin it's always very difficult to express to every possible audience quite how busy & complex a job you have, not least in today's environment where you have wired and wireless connectivity from every imaginable device, uPnP, SSDP, ARP, netbios, Active Directory, DHCP, DNS, UDP, TCP... It's a plethora of fields you have to take collectively as knocking on the proverbial door to your network adapter.

Recently we've employed the excellent Solarwinds tools as a method of network node and inter-connectivity debugging, and as much as I enjoy presenting the truly informative flow-charts and information they don't show quite how huge the amount of data and number of packets flying around is.... I therefore set about visualising and displaying just such a situation to an audience...

A Ubuntu VM, with the I3 desktop and a little time later.....

cd~
git clone https://github.com/the-tcpdump-group/libpcap.git
cd libpcap
./configure
make -j4
sudo make install

Then...

cd ~
git clone https://github.com/the-tcpdump-group/tcpdump.git
cd tcpdump
./configure
make -j4
sudo make install

And now, I could... "tcpdump"... to just spew everything into a terminal window...

Open another terminal window and I could "tcpdump | grep 'facebook'" and see how much time people were flying off to facebook, the beauty and simplicity of the i3 desktop along with the raw output of tcpdump soon conveyed far more stark a message from a monitor on my desk than any e-mail could or diagram could communicate.

Just the TCP packet headers were enough, without prying into what was being sent over a company network, in company time to facebook... and ebay... and whatever else... 

Using egrep I could dig even further into the headers and get very specific, laying out the desktop with i3 just further emphasising the flow and pattern of usage... Anonymize it and I'd have a decent techy screen-saver too!

Monday, 28 November 2016

The Xeon Hack is Dead, Long Live the Xeon Hack!

Whilst investigating a problem with the Socket 775 to 771 Xeon hack machine I found it would no longer boot, it then would no longer post, and finally would no longer even accept power (indicated on the 3v rail LED)... This was a disaster, I've been sorting out the network at home for the last few weekends, and yesterday morning was meant to be a delve in & fix session (at 830am on a Sunday, this is a feat).

Unfortunately it immediately escalated, the motherboard showed distinct signs of corrosion, which is really strange as it's been in a dry airy room, there looked like (and tasted) like salt condensed on the board... I do wonder if this board had had a life near the coast in former days (it was second hand), and the salt just slowly precipitated out of the fibre glass?

Whatever the reason, there was salt all over the board, I cleaned it all with isopropyl alcohol to no avail, it would not post.

So I stripped it out and went to my junk pile, two other motherboards were already dead, the third... Well I know it works, after a fashion, it's an EVGA nForce 680i SLI board, my previous main workstation board actually... But I retired it for my Core i7, and it had been off with a friend of mine, it has at least one faulty RAM slot too...

Inserting my test Celeron D it came on, and I could run a memory test until it overheated and thermal shutdown occurred... So, I pulled out the Xeon from the hack board and got it into the nForce... Nothing... Dead... But, a BIOS patch later (with a floppy disk!) and everything was working...

So the Xeon went into the EVGA nForce 680i no problem!  4GB of RAM installed in the two working slots, and with new thermal paste I left it soak testing... Everything seems fine...

And this is equivalent (if not better) than the previous board, because I know its history, it's got six SATA headers dual gigabyte LAN... It's actually the perfect little server board, except for the lack of the working memory slots.

A new one of these boards is still like £50, so that was out of the question, I did order a new one from ebay a Gigabyte branded on, which can take up to 16Gb of RAM but only has a single LAN connection, it will have to do.

Until then though, the server is getting re-installed on the EVGA nForce 680i, and I'm going to keep my eyes on ebay for another of these boards to replace the already dead set from my junk pile.

On the topic of drives, I wanted to set up a series of physical mirrors with ZFS, however, I don't have matching drives, so I'm wondering what's the best order to set up the disks...

I feel a little confused as to the best way...


Thursday, 10 November 2016

My Home Network

My home network has been neglected, this is one of the problems of working in Technology, when you get home you are not going to be doing very much technology... Or maybe I'm just too interested in other things... Whatever the reason, neglect has set in.

Lets take a look at my home setup:

The network is broadly speaking split into two, the parts downstairs and the parts upstairs.

Downstairs is pretty much the Cable Modem box, a home hub set to Modem Only mode, connected to a Linksys router with some network attached storage for dumping files or media.

Upstairs is where the trouble begins, the critical path is to the left two upstairs items, my Xen server and especially my main Workstation, without these I can't work at all.  So thats two connections which I do not mess with, moving down we see the dotted yellow line, this is a single cable which lays on my desk that pays double duty to my powerful laptop or a raspberry Pi, so that's a spare I generally always need around.

We've used up four of our eight ports on the switch.  The final four are each going to the DRACs on my Dell Servers, which means they have no data connection.  If I want data to them (which is pretty much every time I use them) I either pull the wire from a neighbours DRAC, or I pull the cable from the IP Camera; it being the eighth and final port on the switch as it stands.

I have to ask what my options are... Well, I'm not able to change the cable trail from the lower to upper floor, so only one Cat6e cable there still, which means its not yet work my moving a box downstairs and dedicating it to pfSense & Squid.

I also don't have any rack space, so a racked switch with more ports is really a waste of money at the moment.

I took a look at another Netgear GC108 unmanaged switch, but I wondered about sub-net masking out some of the server stuff and thought for the few pounds different I'd go for a managed switch.

The desk then gets a new dedicated managed switch, and the more server stuff all stays together on the unmanged switch...


With the Dell servers immediately taking up six ports between their DRAC and data NICS I have two left, one for the Xen server and one to cross-connect with the managed switch.  When I come to rack these machines in a better manner, then I'll be able to co-locate the 8 port switch into whatever solution I have there without rewiring my main working station & desk!

This leaves me two ports free at the desk, in a unit which is light and small enough to screw to the underside of the unit (no way I could do that with a larger unit).

The real beauty for my needs here is the switch interlink, I can unplug just one wire and take away all my servers for re-positioning or remounting.  I could even take them all out of my immediate workspace now and hang them off of the WRT1900 downstairs (as it has two RJ45 ports spare).


Note to all the haters... On the topic of the Linksys WRT1900ACS, there is a lot of talk on the internet of it being flaky, unstable, crashing, resetting to factory defaults... Mine has been nothing but stable, like really stable, it's been reset once due to my needing to clear the cumulative six months of network map details and I think it locked up once with the WiFi not coming online.  This doesn't mean to go out there and buy one (though I did review it on Amazon, go take a look) but rather the unit I have was very good, and remains very good.


P.S. Neither Netgear nor Linksys sponsored my usage of their equipment, but you know, if you want to... Get in touch at the link near the Tip Jar!

Thursday, 27 October 2016

Administrator : Linux Network File System (NFS) Mounted Drives

Over the next few days I'm planning to bring you at least three videos about sharing files between different systems, specifically Windows and Linux... Today the easiest (at least for me) Linux to Linux sharing.

For this you will need SSH access and a user account on the remote system, and sudo (root) rights to both machines.  I'm running Ubuntu machines here, both for the client and the server, which variant (32/64) makes no difference.

The Server
sudo apt-get update
sudo apt-get install nfs-common nfs-kernel-server

We need the nfs-kernel-server here, and it will run as a service, once it's all installed we need to make a folder, I create them like this, making it owned by myself:

sudo mkdir /media/xelous
sudo chown xelous /media/xelous

Then I edit:

sudo nano /etc/exports

And I add to it:

/media/xelous     150.0.8.*(rw,no_root_squash,async)

This is the local folder we're mounting, and we're making it available to ALL the machines on the "150.0.8.1 to 150.0.8.255" range of IP addresses.

Saving this file, I then need to restart the whole machine, or just the service:

sudo /etc/init.d/nfs-kernel-server restart

You can then run:

showmount -e

To see the local mount you've just created, if you have an issue, and it doesn't show up, check the above again... because it does work, honest.... The most common problem is permissions on the folder you've created, sometimes on systems you are not the administrator on, it's best to share a folder from your /home directory.

The Client
The client is a simpler installation:

sudo apt-get update
sudo apt-get install nfs-common

Then you can check the remote mount, lets assume the server is on IP 150.0.8.40:

showmount -e 150.0.8.40

You should see the remote mount you created on the remote machine:

Lets create a folder locally, into which we'll mount the remote folder:

sudo mkdir -p /media/remote
sudo chown xelous /media/remote

Now, I happen to be the user "xelous" on both machines, but change your username for the local or remote machines... Mine is not best practice here, as they just have different passwords....

To mount the remote folder locally:

sudo mount 150.0.8.40:/media/xelous /media/remote

So, this is mounting the remote to the local, on the local machine I can then just hop into that folder and work, knowing all the files are trickling out over the network and into that remote machine.

This is very useful if you're going to run a thin client system, or are working on a machine with no, or read-only, local storage.

Why does this exist?
The driver behind this was my main development machine running out of disk space, and my not being allowed to install a new drive... yes, go figure (don't worry, I have asked the fair fellows of IT for access to my BIOS again - Yes, I'm still on a machine with a BIOS not UEFI, don't laugh).

So, with my workstation critically low on disk space, where was I going to put everything?... Well, on another Linux machine I have on the network of course, a big fat server with a slow CPU but oodles of storage.

Friday, 9 September 2016

Story Time : Fantastic Rack Mount Mistakes #3

Technically this is not a rack mounted mistake, but it was a mistake made by someone with a rack mounted unit.  A loooooooottttttttt of years ago, around the turn of the millennium in fact, I worked at a company where they used a Windows 2000 Server to collect a series of information, from memory, I think it ran Websphere and Jakarta Tomcat as middleware, connecting to a Microsoft SQL Server back end.

This server gave me nothing but trouble, I had to bring it down to publish new software to it, then bring it all back up again, because of some wierdness, and worst of all, I was only a user on the machine, I never saw it, was never in the same room as it, it was hosted in a data centre far away from me.

Remoting into it on late 1990's internet (because they'd not upgraded) was painful at 14kpbs, so much so that connecting to it from home was easier, where I had the first generation "Diamond Cable" (later NTL, later Virgin) broadband... at a blistering 512Kbps.

The main problem was, I needed someway to get the server to tell me it's IP, it could change, and the network guy at work used to handle this by crystal ball gazing, and copying the new IP into an e-mail and sending it to everyone.  Of course at home, I didn't get my work mail... Humpf.

The system however was all just Java, and after about 18 months I got the chance to move up the suckling chain of management within the project, and I immediately pointed out to the directors that we could drop all this Windows stuff, and the expensive licensing, by going to this new system called "Linux".

As a result I ended up at an open day presentation in the middle of Birmingham, with speakers from RedHat and Suse.  The talks were pointless, the guy from RedHat wore a T-shirt saying "Suse is shite", and the guy from Suse wore a suit and talked about professionalism; not very constructive, it all wanted to pull the admins in the room into the "are you a pro, or are you a hacker" division.  Neither talked about the distribution.

I therefore decided to learn about Linux myself, and I started a new server, initially just an old Pentium II machine with 32Mb of RAM, it was soon found to be a little bit better and a hell of a lot cheaper than the Windows Server, so I got a new shiny machine (my first commercial rack mounted server, I forget the model, I'm pretty sure it was a Compaq, as I'd seen the Proliant at my previous place of work and think I told the boss to get one).

This machine arrived, and it ran seamlessly pretty much from the get go, as had a couple of disk deaths in it's time, but there was no problem with it.

With the problem of it being in the remote location however, I had a trick, I created a script, like this:

ifconfig > config.txt
traceroute www.bbc.co.uk >> config.txt
cat config.txt | mail -s BootMail xelous@hotmail.co.uk
rm config.txt

The result?... I had it send me a mail whenever it reset, so I got the IP information, and a trace route listing to the outside world (I think the original place I used to trace route to was Altavista!  And it didn't go to hotmail, it went to my old NTL provided e-mail address.

What's the mistake here?... Well, that NTL e-mail address linked to my virgin e-mail address, which forwarded to my MSN address, which turned into Hotmail.

And... You may have guessed it... The other day, that very server was turned on somewhere, somehow... It had a network connection, was powered on, and it sent me a mail!

It was in Worcestershire, I think, and I could still SSH into it!

I changed the daily greeting to tell them they're server is insecure, disabled the script which was e-mailing me, and this pretty much ends our story.

The failure?  Don't plug things into your network, into your rack, unless you know what they're trying and going to do.  EVER!

Monday, 8 December 2014

The Hack

I've been off work, obviously with my feet, however, I've also been off because I've moved house, which took just over a week.  There are a couple of bits and bobs left at the old house and the sale is progressing, whether it all gets done for Christmas and the wife and I can actually celebrate is anyones guess.

Those events are however not what I want to talk about today, no todays topic is one of the systems under my control being the subject of a hack, a successful hack too.

I've been in this game a long time, I've administered Unix, VAX VMS, Sun Solaris, Windows and Linux servers, I've seen access attempts, heard social engineers (cold callers) and even found evidence of folks trying to pick locks to server and switching equipment cabinets.

Until this hack however I'd never lost control of a machine, never had any damage done, and never expected such a strange attack.

The target machine for these problems was a Windows 7 32 Bit virtual machine, being used as a development box with an externally open port to a fixed IP on the local LAN, which the IT Admin had wired upto the company external IP Address and a third party company routed a tunnel through our firewall.

Through this single IP/Port combination the Windows machine was compromised...

Oddly, and quite annoyingly, the IT Admin immediately pointed his finger at one of the pieces of software I was running "Apache"... Could you imagine the uproar in the world at large if Apache web server had a vulnerability which allowed the kind of hack I'll detail later?... Let me just say, I ribbed him back about it, but his inert and instant finger pointing away from what I believe the true problem child annoyed me.

The other software being run on the machine was Visual Studio 2013, whether that is vulnerable, I don't know, perhaps however one would expect some evidence that online/connected services being used by Visual Studio were accessed, some log or trace, and there aren't any, the only traces left were in the Windows logs (event viewer).  Reinforcing my annoyance at the finger being pointed away from Windows.

The user software being operated did not contain any code to do the actions carried out on the machine, indeed only Windows contains the ability to do what was done, so this was the final nail in the coffin for me Windows was to blame.

What was the hack?  You know what, I have no idea, having gone through the evidence and checked I have no idea what allowed the activity, however here's my general pattern pulled from the event viewer.

Thursday 13:30  Machine left in Idle.
Friday 03:01  External Access Logon Requested
Friday 03:03  Logon negotiated with null GUID

(This logon was never listed as successful, only that it was negotiated, I therefore suspect an IP Spoofing attack or some kind).

Friday 03:04  Logon elevated to grant all tokens

Whoever this was, they spent about three hours poking about insude the machine, then logged off.

Saturday 03:01  Logon negotiated with null GUID
Saturday 03:01  Logon elevated to grant all tokens
Saturday 03:03  All user accounts set locked
Saturday 03:13  Volume Shadow Copy started
Saturday 03:23  Volume shadow Copy crashed
Saturday 03:24  Unknown Application reported 100% CPU
Saturday 03:38  New user account created with name "hahaha"

Several more shadow volume copies occur, then this person logs off.

Sunday 04:13   hahaha logs on
Sunday 04:15 All user accounts set to disables, except hahaha
Sunday 06:38 hahaha logs off
Sunday 06:39   Machine shutdown by hahaha

That's what they did, not a lot I admit, however, we have the times this happened, we have the Event View log as proof, and we pay a company to look after the company firewall... So they have access logs right?... Right?... RIGHT?...

Nope, apparently it is too much hassle to check the logs, and according to one source "we get port scanned 100 times a day, what's the point of chasing down one hack?"... erm because they got in... they didn't just scan they got in, and for the life of me I can't figure out how.

Windows was patched, firewall was on, only a none-standard port was open and it was only listening with a custom application with a specific and narrow role to carry out...

Everything else on the machine was not available to that port, or on the second network adapter in the machine!

Thursday, 23 January 2014

Network Guru Fails at Monitoring his own Bandwidth

Do I come on here to bemoan the seeming incompetence of others a lot?... Because I have  just had an annoying 20 minutes talking to one of our "Network Experts", there's a server box running Ubuntu, its actually a virtual machine, and it was being blamed for crippling the network on the host machine - which has to run several other Windows Server 2008 Virtual Machines.

For some reason, this came across my desk, because someone has decided that though I can't advise the company on Linux server usage or adoption, I can be called into sort out the problems other fools create.

So, this server was running, the administrator chap is sat there with PuTTY connected to it and he's saying there's too much network traffic coming from the box.

Looking at the process list the machine is doing nothing, when I ask for one of its users to be made to use it, the CPU usage is a time flitter and then the usage is over, it appears to me the Virtual machine host is waking the VM, using it, and closing it.

The processes being used are simple webservices, so there should be no network traffic unless someone is using the server.

So, I ask.. "What's your idea that this machine is causing the issue?"  Very smugly the admin presented me with an A4 sheet with two graphs, one shows all his servers running with the Ubuntu machine present, and there's a whole load of traffic going on... The next is the same graph, with the Ubuntu box removed, and there's nearly no network traffic.

Then within PuTTY connected to the box he opens iptraf...


And he points to the statistics and declares, "See, this is running multiple kilobytes a second"...

Lets recap... "This machine is crippling our network usage on this box".... "using up kilobytes a second"... If any of you don't grasp how absurd this is please stop reading now, because the guy was clearly serious.  He's not that old, he's younger than me, surely he realises kilobytes a second on a modern gigbit backbone is nothing?  No, he seriously wants the ubuntu box silent.

So, what's causing this tiny trickle of bandwidth... Of course, he's connected to this machine with PuTTY...

"Close this window and take me to the machine in the server room"

In we go, and from the console plugged into the machine I run iptraf... look what we see now...


Yes, its zero...

When he is running his measures and checks he's connected over the network to the machine, he's been measuring his own bandwidth administrating the machine, and apparently the kilobytes per second that took were too much for him, I feel like this guy should be thrown from the building, not be earning far more than me in the "superior" position of "network guru god" which hs holds...

So knowing the machine is idle, I wonder what causes the bandwidth, so with the iptraf still running, I call up the user and ask him to get working again... and sure enough there's little trickles of bandwidth from the Ubuntu box, no spikes, no major blocks of transmission.  Hence after a few minutes I conclude the Ubuntu box though active, is only taking a tiny amount of the total bandwidth available to the machine, and so I start to look at the other machines...

And with just perfmon on the two Windows Server 2008 boxes with the user operating his end, I can see that the Windows boxes are spiking their network traffic, just with task manager you can see one box taking 20% the total available to it, and the other over 45%... This is a gigbit connection, and 20% of it is taken for maybe 30-50 seconds each minute and then goes quiet, then the 45% hog is there for maybe every 10 seconds of each minute.

They're scheduled tasks, as the users input items into their programs, the programs process and send out instructions, e-mails and update other databses.  The trickle of data I/O to the ubuntu machine is just such a feed, the Ubuntu box sucks/queries data from MS SQL Server on one of the machines and squirts it into MySQL where a very old (like 8 year old) unmaintained program written in C with MySQLConnector picks it up and uses sendmail to e-mail a load of people.  Such notifications take maybe 0.25 seconds and run every 5 minutes, the amount of data is small, and looking at the physical name of the Ubuntu box "e-mailer relay" I think it's safe to say its not using a lot of bandwidth and the other machines are to blame.

How I educate the "network expert"... This is my next task.

Sunday, 1 September 2013

Upgrading to 5ghz

I've been using my N-class router in single band mode quite happily for months, however, the street has taken a change of residents there are four new younger couples, and along with them have come more and more wireless networks - all on the 2.4ghz band.

Now, I had been being a bit sneaky and watching the bands being used, and switching to the quiet channels.  However, there's a whole flood now, on channels covering the whole spectrum.

The result has been a whole series of slow-downs, drop outs, and poor network performance on my systems, except for my laptop - which was using the higher 5ghz band on the router.

So, I've stuck a new 5Ghz card into the PC.... Lets see how it goes.